Articles March 28, 2023
The Password-less Future is Closer Than You Think

Say Hello to Passkeys

Legacy Username and Password Authentication
Password-less Authentication with a Passkey
Rapid Adoption; Longer Transition
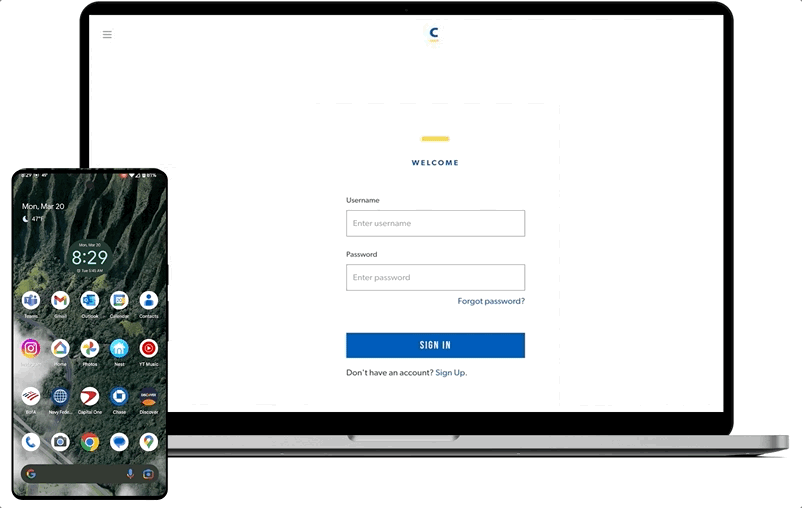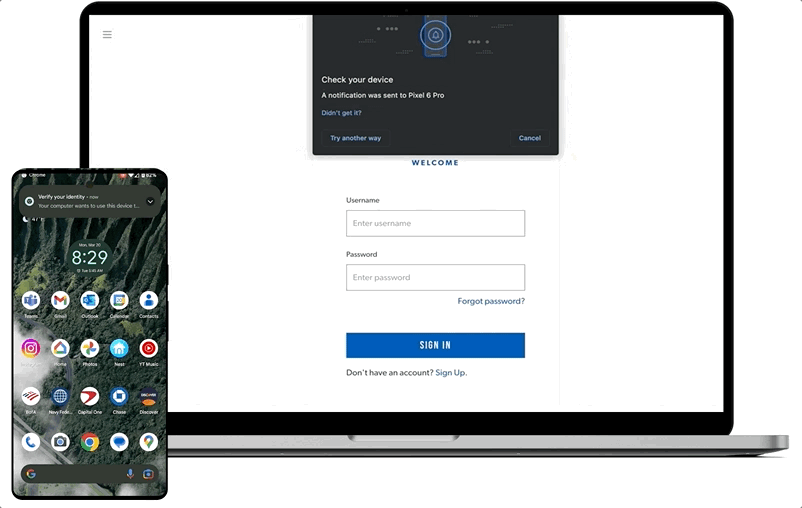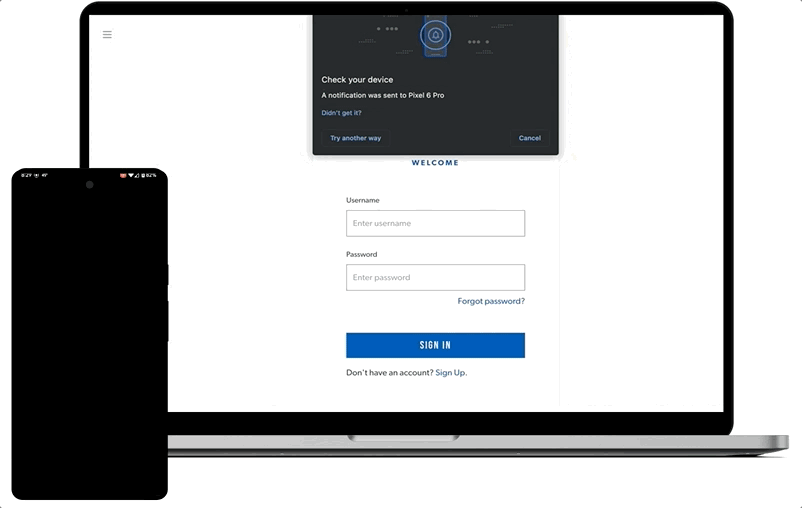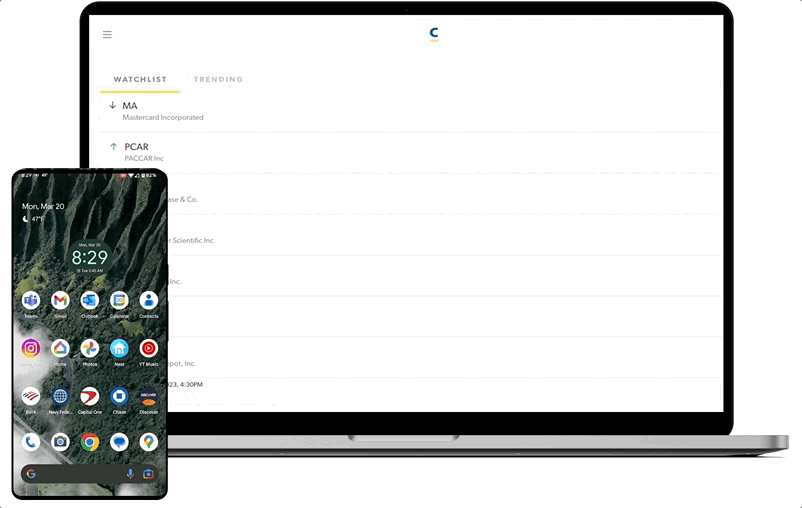
Password-less Authentication using a Passkey from a Nearby Device
Passkey User Flows
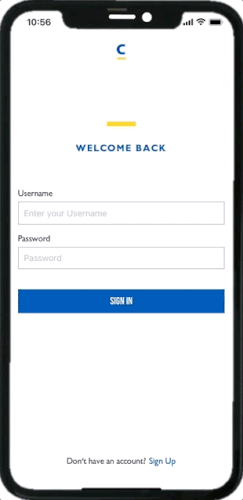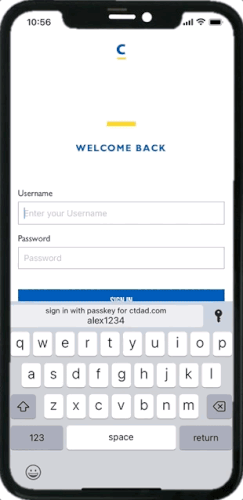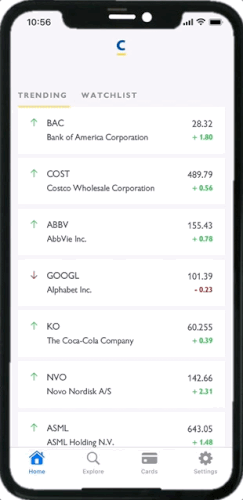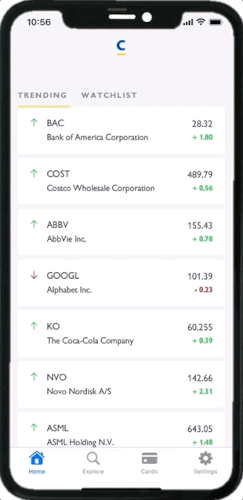
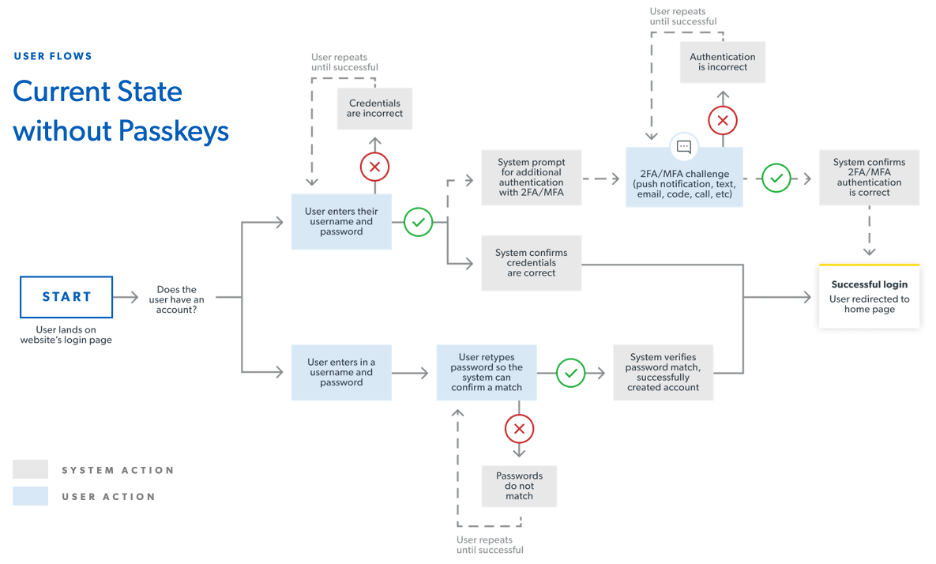
The first flow shown below is one with which every user and organization with a presence online is familiar and has come to accept as a requirement to keep data safe. Organizations have pushed features such as Two Factor Authentication (2FA) and MFA onto users in the name of enhanced security; however, these flows add friction to the user experience and can impact conversion rates and user frustration.
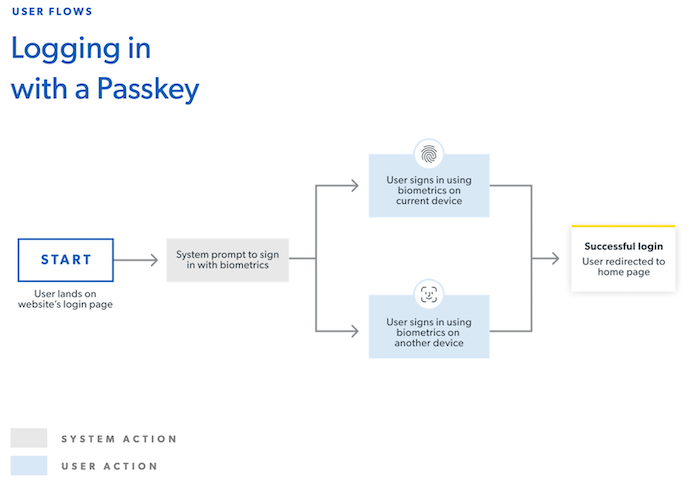
In comparison, as shown in the second flow, the login process with passkeys is much more streamlined, removing the need to type, remember, or store passwords. Furthermore, common 2FA and MFA flows are no longer necessary due to the heightened security that passkeys enable.
A Password-less Future
A Password-less Future with Passkeys Podcast
Listen to CapTech Trends
Mary Deering
Manager
Mary is a project manager with 11 years of strategic communications and project management experience. Her experience includes strategic planning and project management to advance corporate priorities, requirements and business process analysis, and change management.


Mark Badger
Principal, Customer Experience
Mark is a seasoned experience design leader with over 20 years' experience in interaction and conceptual design, product/brand strategy, user research, and information architecture. He is fascinated by what drives people’s connections with brands and is dedicated to fostering value-infused interactions between them.

